

Double Counter, a popular verification bot for Discord servers, was breached on 4 October 2026. If you've ever joined a server that asked you to verify with Double Counter, your Discord username and IP address may be in the stolen data. If you've ever signed in to its website or dashboard, your email address may be too.
Discord itself was not hacked, and no Discord passwords were taken. Here is what happened, how to check whether you're affected, and what server owners should do this week.
At a glance - When: 4 October 2026, for just under six hours - Exposed (operator's figures): about 28 million Discord IDs and usernames, 27 million IP and rough location records, and about 1 million email addresses - Published online: 274,922 email addresses, according to Have I Been Pwned - Not exposed: Discord passwords, stored card numbers or login tokens, according to the operator - Discord's response: new installs of the bot are paused while Discord investigates
What Double Counter is
Double Counter is a third-party bot that screens people when they join a server. It checks new members for alternate accounts and VPN use, which is why it stores IP addresses and rough location data. That makes it useful for keeping raiders and ban evaders out, and it's also why this breach involves so many accounts.
What happened
According to the incident report from Tellter SAS, the French company behind the bot, an attacker exploited a vulnerability in an analytics tool running on a legacy server. Have I Been Pwned names the tool as Metabase.
| Date | What happened |
|---|---|
| 4 October | The attacker spends just under six hours inside Tellter's cloud systems and copies about 12 GB of data. They also take the bot's token and use it to post invites to their own server in around 50 large communities. |
| 4 October | Tellter resets the bot token and restores the service the same day. |
| 5 October | Tellter publishes its incident report and notifies CNIL, France's data protection regulator. |
| 7 October | Have I Been Pwned adds the breach after part of the data is posted publicly. Discord pauses new installs of the bot. |

The attacker got in through an analytics tool on an old server, not through Discord. Photo: FlyD on Unsplash.
What data was exposed
The numbers depend on who you ask, and that's worth understanding. Tellter's report describes everything the attacker copied. Have I Been Pwned counts only what has since been published online.
| Data | Tellter's count (copied) | Published, per Have I Been Pwned |
|---|---|---|
| Discord user IDs and usernames | About 28 million | Usernames included |
| IP addresses and rough location (country, region, city, postcode, ISP) | About 27 million | Locations included |
| Email addresses | About 1 million | 274,922 |
| Names, countries and postcodes | Some paying subscribers | Included |
Digital Citizen's analysis adds that Tellter says a separate cold-storage database covering about 58 million users was not accessed.
What wasn't taken matters too. Tellter says the data contained no Discord passwords, no stored card numbers and no Discord login tokens.
What Discord has said
Discord says its own systems were not breached. It has stopped new servers from installing Double Counter while it works with Tellter to understand the scope, GameDev.net reports. Discord hasn't said when new installs will resume or whether anything changes for servers that already use the bot.
What you should do as a member
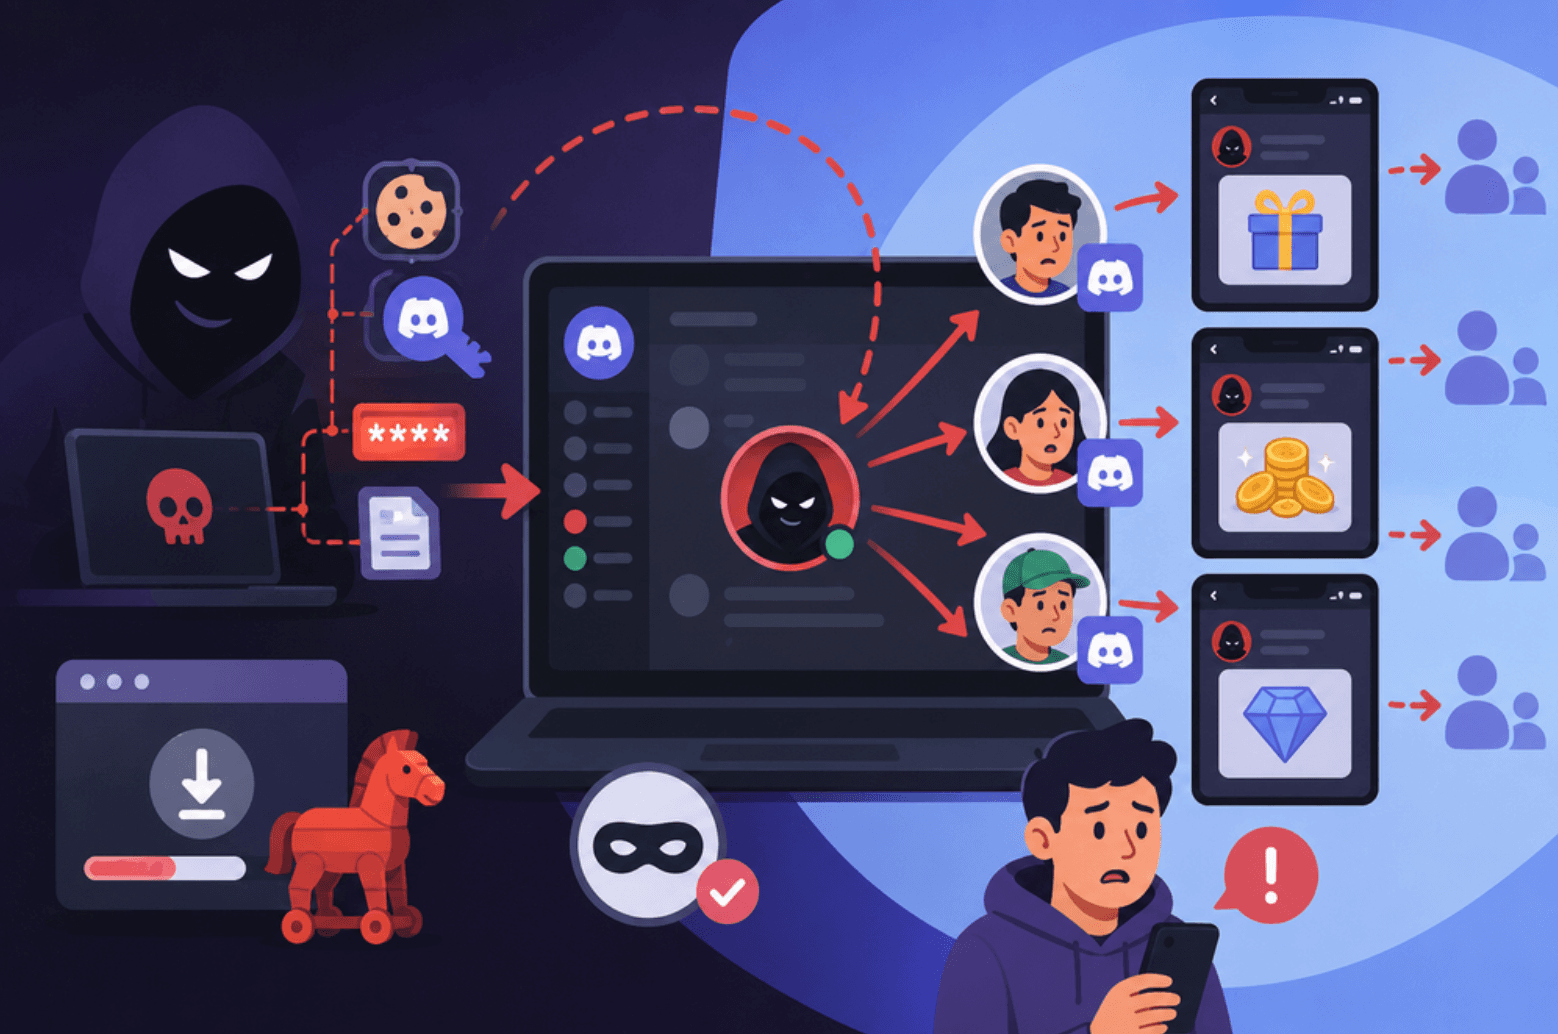
You don't need to change your Discord password, according to the operator. The bigger risk now is phishing, because some email addresses are public.
- Check your email on Have I Been Pwned to see whether it's in the published data.
- Expect fake emails and DMs. Scammers may mention Double Counter, verification or your server to sound convincing. Tellter says it never asks for passwords, tokens or payment by email or DM.
- Don't "re-verify" through links you're sent. Only verify through the button inside the server itself.
- Turn on two-factor authentication on Discord if you haven't already. It won't undo the breach, but it makes a phished password far less useful.
- Remove the bot's access if you want to. Go to User Settings > Authorized Apps and deauthorize Double Counter. This is optional.

Leaked emails usually lead to phishing. Treat any message about "verifying" your Discord account with suspicion. Photo: Brett Jordan on Unsplash.
What server owners should do
If your server uses Double Counter, work through this list:
- Clean up the 4 October posts. Delete any Double Counter messages sent between about 12:00 and 16:30 UTC on 4 October that invite people to another server. Tellter says most were removed, but check your channels.
- Check your audit log for anything the bot did in that window.
- Warn your members. A short pinned announcement explaining what happened, and that staff will never ask for passwords or ID, will stop a lot of scams before they start.
- Review bot permissions. Give every bot only the permissions it needs. A verification bot rarely needs Administrator.
- Decide on verification for now. New installs are paused, so if you were about to add Double Counter, plan around that. Existing setups keep working unless you remove them.

An audit of bot permissions takes a few minutes and limits the damage if any bot is compromised. Photo: Stephen Phillips on Unsplash.
The bigger lesson for communities
Every bot you add holds some of your members' data and some power over your server. This breach came from an old analytics server that should have been locked down, and the stolen bot token was enough to post into dozens of communities at once.

One old, forgotten server was enough to expose millions of records. Photo: Philipp Katzenberger on Unsplash.
That doesn't mean bots are unsafe. It means owners should treat them like staff: know what each one does, give it the least access it needs, and remove the ones you no longer use.
FAQ
Was Discord hacked?
No. Discord says its systems were not breached. The data came from Double Counter's own servers.
Do I need to change my Discord password?
The operator says no account changes are needed, because no Discord passwords were in the data. Turning on two-factor authentication is still a good idea.
Is it safe to keep using Double Counter?
Tellter says it has rotated its secrets, disabled the stolen credentials and moved its databases onto private networks. Discord has paused new installs while it investigates, so many owners are waiting for Discord's findings before deciding.
Why does a verification bot have my IP address?
Checking IP addresses is how Double Counter spots alternate accounts and VPNs. That's why the breach includes IP and rough location data.
Stay safe out there
Check your email, ignore anyone asking you to verify through a link, and if you run a server, spend ten minutes on the checklist above. For more on the scams that usually follow breaches like this, read our guide to spotting fake Discord giveaways.
Want to find well-run communities? Browse servers on Discords.ai.
Sources
- Have I Been Pwned: Double Counter data breach, added 7 October 2026
- Digital Citizen: Double Counter breach leaks 275,000 emails, 9 October 2026
- GameDev.net: Double Counter hit by breach exposing around 1 million email addresses, 7 October 2026
Comments
Sign in to join the conversation
Sign inNo comments yet
Be the first to share your thoughts!