
In September 2026, Anthropic published an unprecedented Threat Intelligence Report documenting state-sponsored misuse and dangerous capability probing across its Claude model suite between December 2025 and August 2026. The report marks a pivot in AI safety moving from theoretical existential risk to operational defense against real-world threat actors.
By cataloging adversary behavior across seven harm domains including conventional weapons development, biological misuse, state surveillance, and model distillation, Anthropic established a blueprint for frontier AI threat monitoring and live API defense.
Operational Misuse & The Frontier AI Threat Landscape
Frontier AI models (such as Claude Haiku, Sonnet, and Opus) offer significant operational uplift to malicious actors by serving as software engineers, intelligence aggregators, and research assistants.
Anthropic’s investigation revealed that state-backed entities actively used AI systems to accelerate targeting files, write missile autopilot software, bypass surveillance warrants, and assist in high-consequence dual-use biological research.
Threat Architecture & Generative Threat Groups (GTGs)
Anthropic tracks malicious activity using Generative Threat Group (GTG) designators.
State-Nexus Engineering Cells: Advanced state-funded teams utilizing agentic environments like Claude Code to automate complex systems development, missile telemetry analysis, and software deployment.
Espionage & Reconnaissance Actors: Intelligence units using language models to parse open-source intelligence (OSINT), structure naval positioning data, and build exploit frameworks.
Dual-Use Life Science Researchers: Scientists leveraging commercial platforms often through third-party API resellers—to query restricted biological topics under dual-use research pretexts.
Key State-Backed Actors & Documented Cases
The Yemen Missile Development Cell
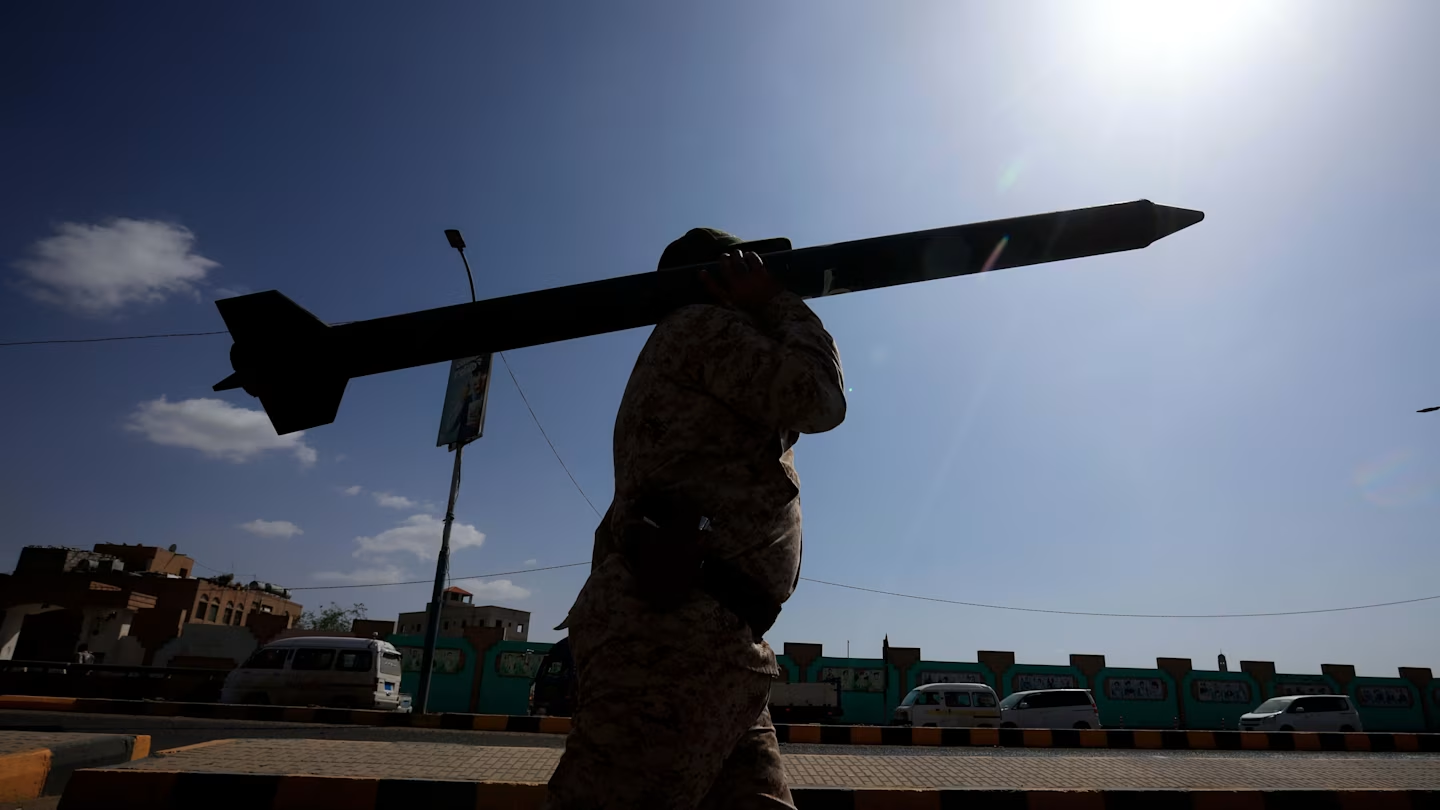
In one of the report's most severe cases, a state-aligned weapons cell in northern Yemen used Claude Code as an automated engineering lead to orchestrate software for three distinct missile programs.
Iran-Nexus Naval Targeting & Surveillance
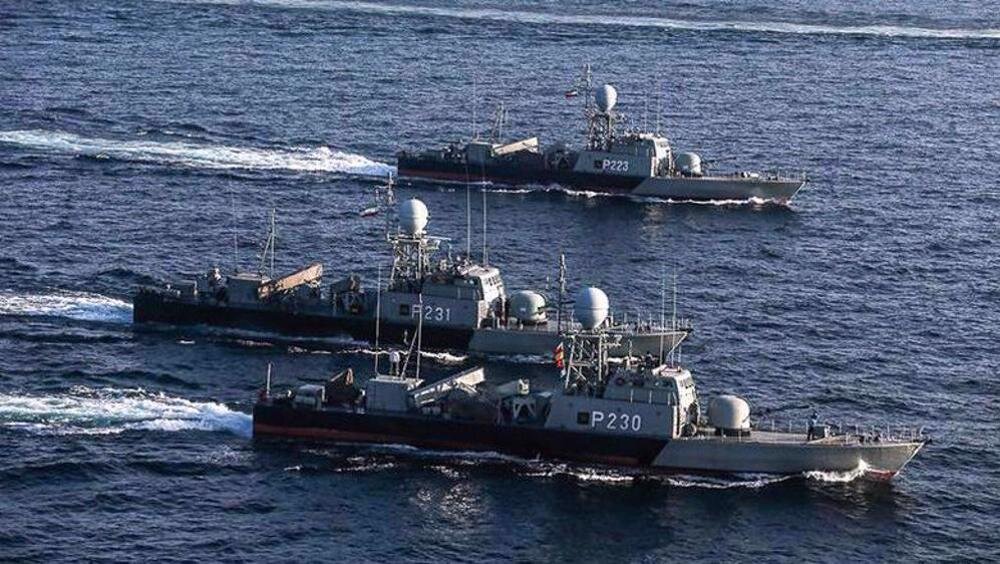
An Iranian state-linked operator constructed a Python pipeline powered by Claude to compile publicly available military photos, satellite imagery scripts, and ship transponder data into real-time targeting files on U.S. naval forces.
Chinese Model Distillation & State Exploitation
The report documented unauthorized high-volume model distillation campaigns originating from major Chinese AI organizations, including Alibaba, Moonshot, and DeepSeek.
Biological Weapon Queries & Dual-Use Risks
Anthropic flagged five distinct cases of biological misuse.
Gain-of-Function Research: In May 2026, an automated biological safety classifier blocked an API request requesting assistance with drafting a grant application focused on gain-of-function work on the Chikungunya virus (enhancing transmissibility and immune evasion) intended for execution at a military institute.
Toxin & Vector Manipulation: Other cases involved viral adaptation models, venom peptide optimization, and toxin redesign queries.
Reseller Platform Exploit: Investigations revealed that several biological queries breached policy by routing through third-party API reseller networks operating in regions where native Anthropic services were unavailable.
New API Safety Protocols & Technical Defense
Following these discoveries, Anthropic implemented an upgraded security framework across its API infrastructure and developer endpoints:
Multi-Session Context Inspection: Advanced classifiers monitor user activity across multiple disconnected API sessions to catch actors attempting to split malicious workflows into seemingly benign, isolated fragments.
Agentic Sanity Check Gates: Agentic interfaces like Claude Code now feature mandatory human-in-the-loop checkpoints, preventing execution of firmware compilation or autonomous system testing when dual-use hardware profiles are detected.
Strict Reseller & Know-Your-Customer (KYC) Enforcement: API key provisioning now enforces rigid telemetry verification on commercial resellers to block unauthorized proxy access from non-serviced jurisdictions.
Real-Time Bio-Safety Classifiers: Automated screening tools evaluate queries involving select agents, viral engineering, and toxin sequences prior to model generation.
Platforms and Availability
The threat intelligence mitigations and updated safety controls apply across Anthropic's enterprise endpoints and commercial models:
Claude API (Haiku, Sonnet, Opus tiers)
Claude Code (Agentic CLI Environment)
First-Party Consumer Portals (Claude.ai)
Major Cloud Platform Integrations (Amazon Bedrock, Google Cloud Vertex AI)
Why It Matters
Anthropic's 2026 Threat Report shifts the conversation around AI governance from speculative scenarios to concrete threat intelligence. By disclosing real-world exploits, Anthropic provides governments, civil society, and competing AI developers with actionable indicators of compromise (IOCs) needed to secure the global AI supply chain.
🎮 What to Know at a Glance
| Detail | Information |
| Document Title | Anthropic Threat Intelligence Report (September 2026) |
| Observation Window | December 2025 – August 2026 |
| Key Harm Areas | Bioweapons Probing, Missile Software, OSINT Naval Targeting, Model Distillation |
| Primary Models Involved | Claude Haiku, Sonnet, Opus (widely accessible tiers) |
| Key Security Fixes | Multi-Session Context Classifiers, Agentic Checkpoints, Reseller KYC Controls |
🎮 The Bottom Line
Anthropic’s 2026 Threat Report exposes how state actors, missile developers, and life science researchers attempted to turn commercial AI into an operational engine. By shutting down these operations and hardening its API protocols, Anthropic has established a new standard of transparency and active defense for the entire AI industry.